End-to-end cloud infrastructure, DevOps and security consultant.
End-to-end, cloud-native infrastructure on any major cloud. Architecture, networking, DevOps delivery and security, through to handover.
Azure · AWS · Google Cloud · IBM Cloud · Oracle CloudDelivered as codeHanded over with runbooks
- MicrosoftAZ-305Azure Solutions Architect Expert
- MicrosoftAZ-104Azure Administrator Associate
- 5+ yearsin production on AWS, Azure and GCP
- 50+production platforms run
- GitHubOpen sourceKubernetes MCP server
The short answer
What does end-to-end cloud infrastructure delivery include?
One consultant for the whole cloud-native platform: the infrastructure and network, the DevOps pipelines that change it, and the security that protects it, delivered as code and handed over to your team.
- Architecture, networking and hybrid connectivity
- DevOps pipelines and infrastructure as code
- Security, identity and compliance controls
- Kubernetes and cloud-native services
You need this when
- A move to the cloud, or a second cloud, is being planned.
- A security review or audit is asking for evidence.
- Teams create resources by hand and nobody can say what exists.
- You need private connectivity to on-premises systems.
What you receive
- 01Target architecture and network diagrams
- 02Infrastructure as Terraform in your repositories, including the landing zone
- 03Guardrail policy set with rationale
- 04Onboarding runbook for new workloads
Scope
What the work covers.
Cloud infrastructure designed and delivered end to end: the architecture, the network and hybrid connectivity, identity, security guardrails and shared services, built as code and handed over to your team. The governed foundation is one part of the work, not the whole of it.
End-to-end cloud infrastructure design and delivery (AWS / Azure / GCP)
A foundation designed for the cloud you run, or for several.
Account, subscription and project hierarchy
Accounts, subscriptions and projects organised so ownership and billing are clear.
Network architecture, segmentation and hybrid connectivity (VPN, ExpressRoute, Interconnect)
Segmented networks and private links to on-premises over VPN, ExpressRoute or Interconnect.
IAM, guardrails and policy frameworks
Identity, guardrails and policies that stop unsafe resources being created.
Shared services and workload onboarding
Shared logging, DNS and connectivity, and a repeatable way to onboard new workloads.
Tools and platforms
- Terraform
- Azure
- AWS
- Google Cloud
- Entra ID
 Azure
 AWS
How to buy this
Typical engagement models.
Proof
Where this work has been done.
- 99.2%of 55.8M requests served at the edge in 24 hours, national tourism platformRead the case study →
- 8 weeksto SOC 2 Type II with zero external audit findings, FinTech scale-upRead the case study →
Government · Tourism · Azure
A secure Azure platform for a national tourism digital ecosystem, delivered as code.
A high-traffic tourism ecosystem built on Sitecore, .NET and Optimizely needed standardised, observable and resilient infrastructure across development, UAT and production. I owned cloud architecture, security, networking, CI/CD and production application delivery as Cloud Solution Architect and DevOps Engineer.
AzureSitecore.NETOptimizelyRead the case studyFood & Wellness · E-commerce · Azure
The Azure platform behind a high-volume digital meal-plan experience, run as code.
PractiCal sells personalised meal plans across the UAE through a Next.js storefront, Laravel/PHP backend services and Azure serverless workloads. I owned the cloud and application platform end to end: infrastructure, edge security, CI/CD and production operations across development, staging and production.
AzureLaravelPHPNext.jsRead the case studyEducation · Enterprise · Azure
A secure Azure platform for a large-scale university digital experience on .NET and Umbraco.
A university digital platform serving prospective students, current students, faculty and other stakeholders: programme discovery, admissions, applications and student services on an ASP.NET and Umbraco CMS stack. I owned Azure infrastructure, application delivery, security and production operations.
AzureAzure App Service.NETASP.NETRead the case study
Latest from the blog
Related writing from the blog.
26 Oct 2026 · 5 min read
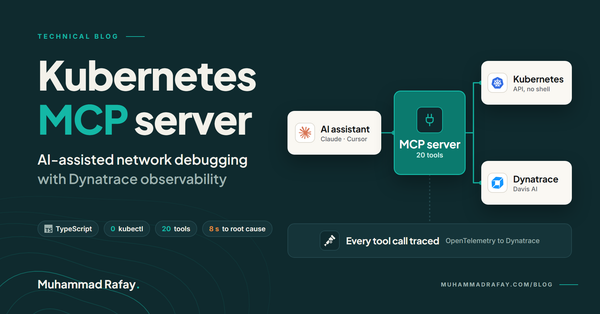
Building a Production-Grade Kubernetes MCP Server with Dynatrace Observability
I enabled AI assistants to access Kubernetes directly for network debugging and to correlate with Dynatrace. The solution uses TypeScript, avoids kubectl subprocesses, and self-monitors via OpenTelemetry.
6 Oct 2026 · 7 min read
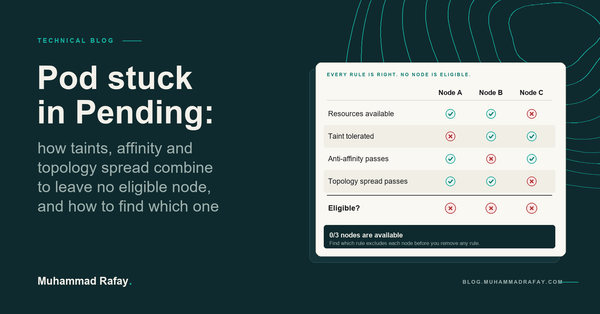
OpenShift Pod Stuck in Pending: How to Debug Taints, Tolerations, Affinity and Topology Spread
A Pod stays Pending when no node passes every required rule, and often no single rule is wrong. How the scheduler filters nodes, what taints, affinity and topology spread each guarantee, a worked example where correct rules combine badly, and a six-step workflow to find the blocking rule.
6 Oct 2026 · 9 min read
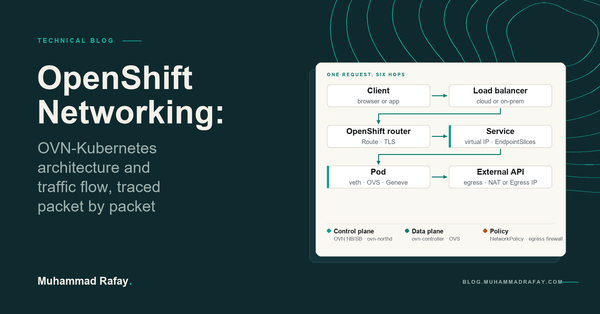
OpenShift Networking Deep Dive: OVN-Kubernetes Architecture and Traffic Flow
Follow one request through an OpenShift cluster: how OVN-Kubernetes turns Kubernetes objects into a logical network, how OVS and Geneve move the packets, where Services, NetworkPolicy, the router and egress fit, and how to trace a failing connection layer by layer.
FAQ · End-to-End Cloud Infrastructure
Common questions.
Still have a question? Ask me directly. I reply within one business day.
What does end-to-end cloud infrastructure delivery mean?
One engagement covers the architecture, networking and hybrid connectivity, identity, security controls and shared services, through to the first workloads running and a handover to your team. The pieces are designed together, so you are not stitching separate projects into one platform afterwards.
How long does it take?
A focused build on Azure or AWS is typically four to eight weeks of fixed scope, depending on the number of environments, hybrid connectivity and compliance controls. The scope, milestones and deliverables are agreed in writing before work starts.
Do you build landing zones with Terraform?
Yes. The landing zone is delivered as Terraform in your own repositories, with pipelines that plan and apply changes through review. Your team can extend it after hand-over without depending on me.
Can you connect the cloud to our on-premises network?
Yes. Hybrid connectivity is designed as part of the foundation: site-to-site VPN, ExpressRoute on Azure, Direct Connect on AWS or Interconnect on Google Cloud, with routing, DNS and firewall rules defined as code.
Can the infrastructure meet Gulf data residency rules?
Yes. Regions, policies and network boundaries can be set so data stays in-country, for example Azure UAE North and UAE Central or Azure Qatar Central, with controls mapped to frameworks such as NESA, NCA ECC, PDPL, NIA and QCB.
Keep exploring
Related solutions.
- SolutionKubernetes & OpenShiftProduction clusters on AKS, EKS, GKE and OpenShift, run with GitOps.Read more
- SolutionAI platform infrastructureSecure RAG and LLM platforms behind private gateways.Read more
- RegionConsultant for the UAEIn-country data residency and NESA controls, delivered on Gulf working hours.Read more
Need a full team or 24×7 operations?
Team-scale delivery is with Cloudlit.
Cloudlit designs, builds and runs cloud and AI infrastructure for banks, government and enterprises: cloud architecture, DevOps automation, Red Hat OpenShift and 24×7 managed operations. When an engagement needs more than one engineer, that is where it is delivered.
Contact
Tell me about the platform.
Tell me what you are building or where your platform is under strain. I read every enquiry myself and reply within one business day.
What happens next
- 01A 30-minute call about your platform and what has to change.
- 02A short written view of the risk and the next step, whether or not we work together.
- 03If it fits, a fixed-scope proposal with deliverables, timeline and price basis.
Prefer to just talk?
Book a 30-minute discovery call, or send a message on WhatsApp. No obligation, no pitch deck.
Or email directly: [email protected] or WhatsApp: +92 332 3600677
Based in Karachi, Pakistan. Working with teams in the UAE and Saudi Arabia.